Are your paperwork processes putting you at risk of GDPR compliance?
Data protection is a major concern for businesses, with one recent survey revealing that over half of businesses (51%) say cybersecurity, data protection, and privacy are their biggest compliance priorities for the next year.
Organisations may be using their data protection budgets to prioritise firewalls, encryption, and access controls. However, while attention is focused on digital data protection, personal data continues to move through the business in a far older and less-guarded form: paper.
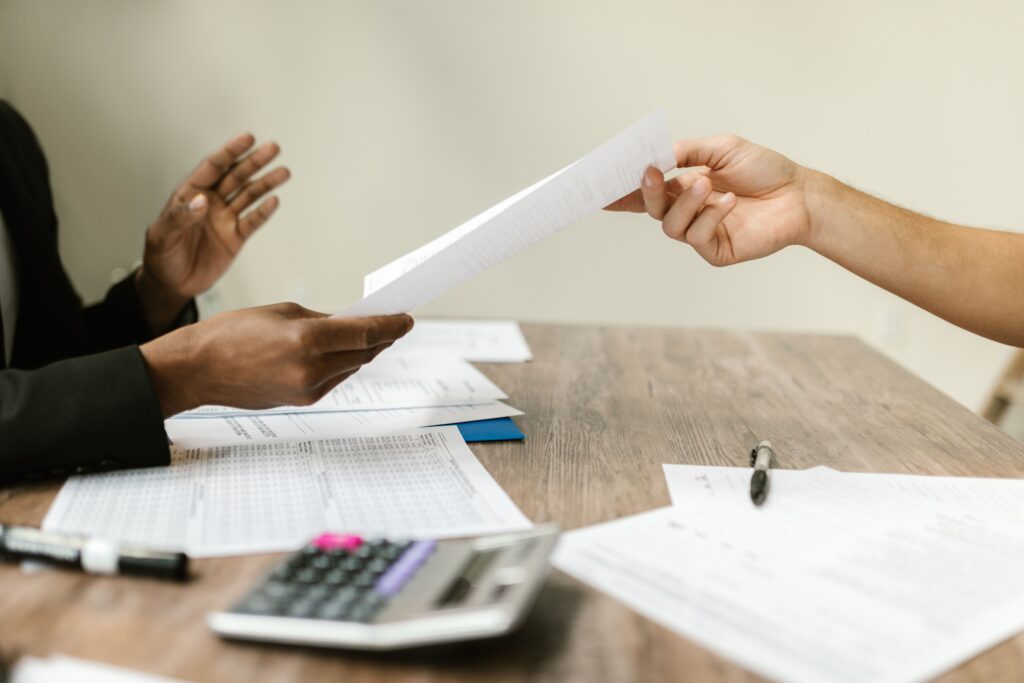
Printed contracts, application forms, meeting notes, visitor books, and archived files all fall within the scope of GDPR and they rarely receive the same scrutiny as their digital counterparts. Unlike a phishing attempt or a ransomware alert, a compliance failure caused by paperwork provides no warning and can be much harder to detect.
The consequences, however, are steep and can include significant fines, reputational damage, and eroded customer trust.
Here are the paperwork habits putting your business at risk and how to fix them.
How GDPR applies to paperwork
The GDPR clearly outlines the types of data that are covered under the act, and how businesses are responsible for safely storing, sharing, transporting and disposing of that data. While businesses have undergone massive digital transformation in the past two decades, many industries still rely on paper documents.
While digital record-keeping has become the norm for many businesses, this does not mitigate the responsibility to safely handle paper documents.
The GDPR does not apply to all paperwork handled by a business. Instead, it applies wherever personal data is held in a searchable form, whether that is a physical record, a printout or a manual filing system in which a name or other identifier can be looked up.
Why paperwork is a hidden compliance risk
While digital data often leaves a record of who accessed it, paper-based failings can go undetected because there is typically no log. A misfiled or missing document may never trigger an alert, so a breach can go unnoticed for months. As there is no access trail, the organisation cannot easily show what happened, or that nothing did. Under the accountability principle, that burden of proof rests with the data controller.
Poor paper handling can lead to unauthorised access, misplaced or unshredded documents, data retained for longer than is lawful, and an inability to fulfil access or erasure requests.
Retaining records for longer than is lawful breaches the storage limitation principle. Similarly, an organisation that cannot locate every copy of a person’s data held on paper cannot reliably answer a subject access request or prove that data has been erased. This reveals that a business does not have full control over the personal data it holds.
Any of these failings can result in serious penalties or reprimands from the Information Commissioner’s Office (ICO). The ICO has the right to impose monetary penalties for failing to properly secure, store or dispose of documents.
While penalties for paper-based breaches are uncommon, the fines can be severe. In one of the largest penalties of its kind, Northern Ireland’s Department of Justice was fined £185,000 for auctioning off a filing cabinet that contained sensitive personal records, including details of a terrorist incident.
More recent cases show the same failures persisting and still drawing action. In 2023, the Ministry of Justice was formally reprimanded after bags of confidential waste, including medical and security-vetting details, were left accessible in an unsecured prison holding area for 18 days because a contracted shredding company had not collected them. Outsourcing disposal, in other words, does not outsource liability.
Fixing your paperwork processes: Strategies for compliance
The first step is for the data controller to put retention and destruction policies in place. These policies should clearly define how long the data is kept and the legal basis for retaining it. The GDPR does not outline specific retention periods, only that data is kept ‘no longer than is necessary’. However, this may vary by industry, so businesses should set a clearly defined period internally. Similarly, it’s crucial to have set destruction policies that outline how paper records should be discarded.
Shredding is typically the easiest method for destroying paper records, but it’s essential to ensure that any identifiable details are effectively destroyed. Where destruction is outsourced, the controller remains responsible, so a written contract and certificates of destruction are essential.
Secure storage, such as lockable cabinets and access-controlled rooms, is also important for protecting sensitive records. Businesses should maintain a clean-desk policy, which requires employees to clear any sensitive documents away whenever they step away from their desk. All physical documents should also have a clearly defined owner responsible for security, retention, and disposal so documents aren’t lost or misplaced during staff changes. With hybrid working now routine, those controls must extend beyond the office to records taken home or carried between sites.
Data mapping exercises can be useful for understanding the full lifecycle of documents in the workplace – from when they are created, to how they are stored and eventually disposed of. This exercise can directly inform how the organisation handles these documents, so there are no points in the system vulnerable to exposure.
Mapping the flow of documents through the workplace can also help identify points where it can be streamlined and made more secure. Digitising document workflows can improve the process by reducing the volume of loose paper, eliminating the need for physical storage areas and strengthening access control.
Digitising can also provide detailed audit trails, whereas paper documents leave no trace of who has accessed them. It can also streamline the retention and destruction policies by carrying out these activities automatically.
Building a comprehensive defence
A strong GDPR compliance policy is only as strong as the staff who follow it. A study on paperwork-related data breaches found that thousands of paperwork-related data breaches have been reported to the ICO in the past six years due to stolen files or documents, leaving sensitive information unattended or losing physical copies.
Genuine paperwork compliance requires more than a policy document or a locked cabinet. Resilience comes from maintaining robust processes, supporting technology, and staff who strictly adhere to data protection policies.
Physical and digital handling should be assessed together, staff should be trained to understand their own role in protecting information, and secure handling should be the path of least resistance rather than an extra step. As organisations grow more digital, the risk is that businesses lose sight of the sensitive data still sitting in paper format.